SecurityWise: Payment Card Transactions and Policies: What Jewellers Need to Know to Be Secure and Compliant
18 Dec 2023
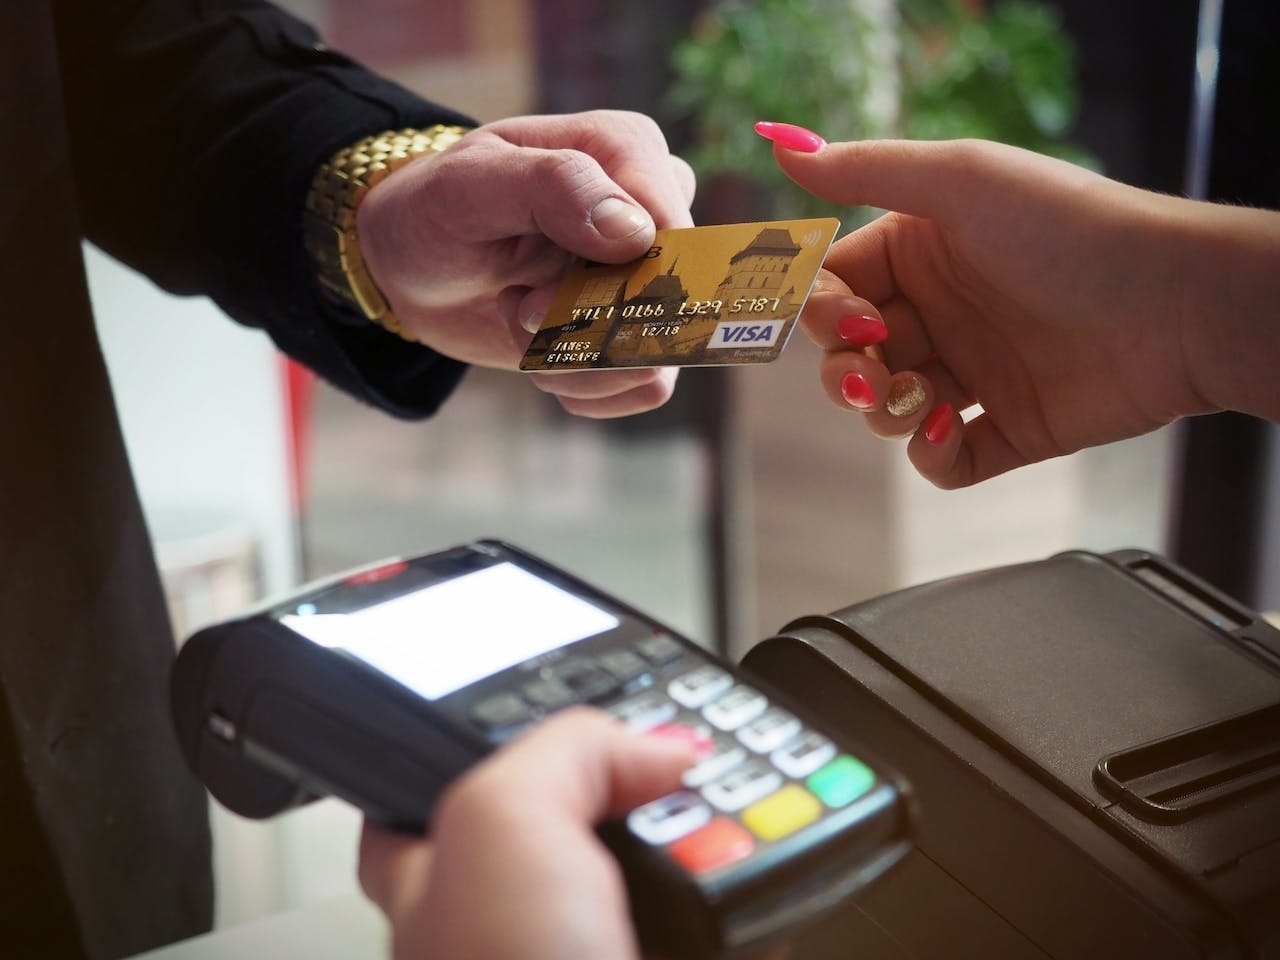
Payment card transactions are a major part of the jewellery business, but they also come with several risks. Jewellers need to be aware of these risks and take steps to mitigate them in order to protect their customers and their own businesses.
One of the biggest risks associated with payment card transactions is fraud. Fraudsters can use stolen or counterfeit cards to make purchases, or they can use phishing scams to trick customers into revealing their card information. Jewellers can help to reduce the risk of fraud by implementing the following security measures:
- Only accept payments from reputable sources. This means being wary of customers who are paying with large amounts of cash or with cards that are not issued in their own name.
- Verify all signatures and IDs. Make sure that the signature on the credit card matches the signature on the customer's ID. If the customer is paying with a debit card, ask them for their PIN.
- Use a secure payment processor. A secure payment processor will encrypt the customer's card information and protect it from unauthorized access.
- Keep your security software up to date. Make sure that you have the latest anti-virus and antimalware software installed on your computers and networks.
In addition to protecting against fraud, jewellers also need to comply with the Payment Card Industry Data Security Standard (PCI DSS). PCI DSS is a set of security standards that are designed to protect cardholder data. All businesses that accept credit cards must comply with PCI DSS, regardless of their size.
To comply with PCI DSS, jewellers need to implement a number of security measures, including:
- Securing their networks. This includes using firewalls and intrusion detection systems to protect their networks from unauthorized access.
- Protecting cardholder data. This includes encrypting cardholder data and storing it securely.
- Educating employees on security procedures. All employees who handle cardholder data should be trained on security procedures.
Jewellers can learn more about PCI DSS and how to comply with it by visiting the PCI Security Standards Council website.
Here are some additional tips to be secure and compliant when processing payment card transactions:
- Limit the number of employees who have access to cardholder data. Only employees who need to handle cardholder data should have access to it.
- Use strong passwords and change them regularly. All passwords should be at least 12 characters long and include a mix of upper and lowercase letters, numbers, and symbols.
- Be careful about sharing cardholder data. Only share cardholder data with trusted third parties, such as payment processors and shipping companies.
- Monitor your transactions for suspicious activity. If you see any unusual transactions, such as multiple charges from the same card or charges from different locations in a short period of time, report them to your payment processor immediately.
Securing both business and customer information is important to all retailers. By following these tips, jewellers can help to protect their customers and their own businesses from the risks associated with payment card transactions.
Source: SecurityWise